Use case
Multi-provider DNS for agencies and MSPs
Agencies and managed service providers look after dozens of client domains spread across Route 53, Cloudflare, Azure and whatever the client already had. RedundantDNS gives you one place to manage them without taking over the clients’ accounts.
The problem
- Client DNS lives in client accounts. Asking for full admin access to every one of them is a hard conversation and a liability.
- Each provider has its own console, record format and permission model. Nobody remembers which client is on which.
- When something breaks at 2 a.m., you want to know which zones are affected and who changed what.
How RedundantDNS handles it
- Each client can be its own organization, with its own encryption key, members and roles (owner, admin, editor, viewer).
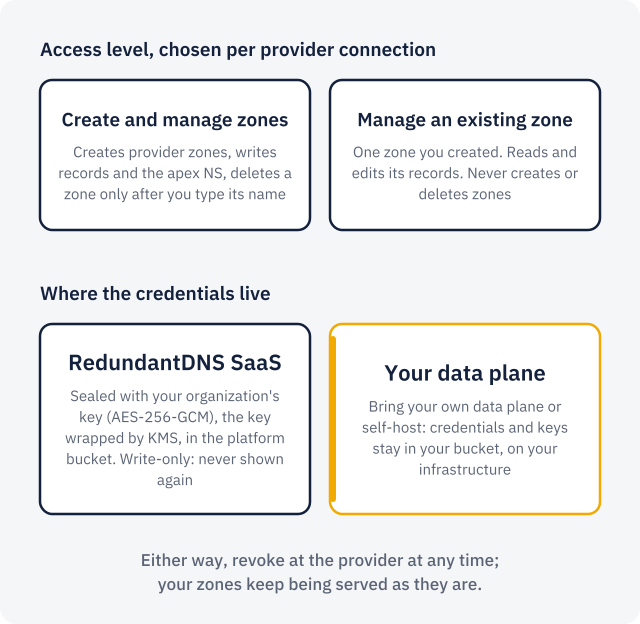
- Credentials stay the client’s: use the “manage an existing zone” access level to touch one zone and nothing else. The key is encrypted on arrival and never shown again.
- Every change is written to the audit log with who, what, when and from where (dashboard, API, Terraform or MCP).
- Alerts go to your channels: email, a signed webhook, or Slack.
The result
One dashboard for every client zone, on the clients’ own providers, with a written trail of every change. Adding a second provider for a client becomes an attach, not a project.
Plans that fit: Pro or Business. See pricing or how it works.
Other use cases
Put your zone on two providers
Start with one zone and two providers you already have. Free, no card.